
RUN
Run Agent Fleets at Scale, Anywhere
Komodor gives SRE, Platform and DevOps teams the control plane to run and manage agents in end-to-end workflows that drive real operational outcomes. Whether self-hosted in the cloud or on-prem, or managed on Komodor Cloud, run one unified fleet, with every agent action orchestrated and recorded.
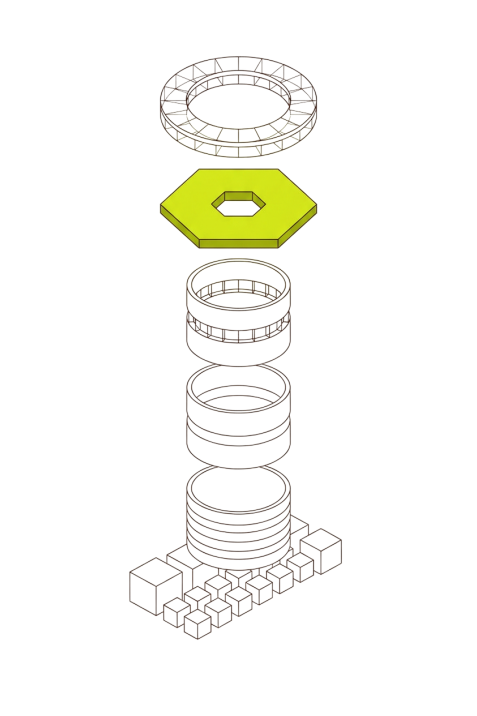
One Fleet, Under
Shared Infrastructure
Every agent running — whether built with Komodor, imported, or pulled from the catalog — is automatically scored, permissioned, and remembered by the same systems as everything else in your fleet.

Build
However it got here. Built from scratch, imported, or pulled from the catalog, every agent lands in the same fleet the moment it’s live.

Run
Wherever it runs, every agent in your fleet carries the same permissions and audit trail, visible right in the fleet view.

Optimize
Every run, already graded. What you’re watching here is scored under the same evaluation engine from its first run.

Govern
Every action, already scoped. What’s running is already permissioned under the same RBAC and approval rules your team set.
Frequently asked questions
Your choice. With the Komodor Agentic Operations Platform you can run agents on Komodor Cloud with no infrastructure of your own, or self-host them in your cloud or on-prem on Kubernetes, VMs or containers. You can also mix both in one fleet. Agents that need to reach private clusters or internal services usually run self-hosted. The control plane can be self-hosted too, for organizations that need everything inside their own environment.
Docs link: Deployment methods
That depends on how you deploy. Self-hosted agents keep credentials inside your network and call internal systems directly. Secrets reach a run in memory and are never written into its record. Each run’s evidence (inputs, tool calls, reasoning, output and usage) is sent to the control plane, so organizations that need all data to stay in their environment self-host the control plane as well as the agents.
Docs link: Deployment methods
No. Komodor agents only make outbound TLS connections to the control plane. Nothing listens for inbound traffic and no ports need to be opened, so agents work behind NAT and in private networks. To reach internal services, you can run an Outpost: a small, outbound-only, deny-by-default relay inside your network that only allows the destinations you list.
Docs link: Network & egress control
Yes. Use Komodor-managed models, connect your own provider credentials, or point self-hosted agents at your own gateway. Supported providers include Anthropic, OpenAI, Azure, Amazon Bedrock, Vertex AI and Gemini, and supported gateways include LiteLLM and vLLM. You choose the model per agent and can change it as the market moves without re-platforming. When you route through your own gateway, inference requests don’t pass through Komodor’s model gateway.
Docs link: Providers
The way your team already works. Agents can start from an alert or any system that calls a webhook, on a schedule, from a Slack message or chat session, from a step in a workflow, or when another agent delegates to them. You can also run them manually. Every trigger produces the same thing: a run with a full evidence trail.
Docs link: How Run works
Yes. Connect Slack, and your team can start agents, workflows and incident pipelines from the conversations they’re already having, with results posted back in the thread. Agents are also available through resumable chat sessions in the Komodor console, and programmatically through the API and MCP server.
Docs link: Channels
After each run, an agent proposes what to remember, such as a root cause or a fix that worked. A reviewer agent checks every draft and removes duplicates before it’s published. Memory is private to each agent by default, or shared between agents you choose. You can see, edit and archive every memory, so future runs build on what worked instead of starting cold.
Docs link: Memory
The knowledge graph is a live map of your services, owners, dependencies, deploys and data stores. The platform keeps it current from operational activity, so you don’t build it by hand. It sits next to two things you control: the knowledge base, where you upload runbooks and service docs, and agent memory. Together they give every agent the same picture of your environment.
Docs link: Knowledge base
No. Agents on Komodor Cloud need no infrastructure of your own, and self-hosted agents can run on Kubernetes, VMs or containers. Kubernetes is one of many environments the platform’s agents can investigate and operate. It isn’t a requirement for running them.
Docs link: Deployment methods
Yes. Everything the console does is available through Komodor’s versioned REST API and its MCP server, under the same permissions. You can also declare platform resources as Kubernetes manifests in source control and let an in-cluster operator reconcile them. Changes then go through your normal review process instead of the console.
Docs link: Developer tools

